How to Build a Secure Business Web Application: The Enterprise Hardening Guide
A practical guide to OWASP Top 10 defense, zero-trust authentication, SQL injection prevention, and cryptographic data protection.

- 1. The Modern Threat Landscape for Business Software
- 2. Mitigating the OWASP Top 10 Vulnerabilities
- 3. Secure Authentication: Tokens, Sessions & MFA
- 4. Database & API Security: Parameterization and Rate Limits
- 5. Hardening Browser Defenses: Security Headers & CSP
- 6. Security Threats vs Defensive Architecture Matrix
- 7. The 10-Point Enterprise Web Security Checklist
In the digital economy, security is not a feature you add at the end of a software development sprint; it is an existential requirement. Every day, automated bot networks, credential-stuffing scripts, and malicious actors scan business websites and client portals searching for vulnerabilities: an un-sanitized SQL query, a leaked API key in client-side JavaScript, a missing rate limit on a login form, or an insecure direct object reference (IDOR). A single data breach can result in catastrophic financial liability, regulatory penalties under GDPR or DPDP regulations, and irrevocable destruction of customer trust. Whether you are engineering a B2B wholesale submission portal, an internal ERP dashboard, or an e-commerce platform, security must be woven into every layer of your codebase. This guide details the essential engineering practices required to build fortified, secure web applications.
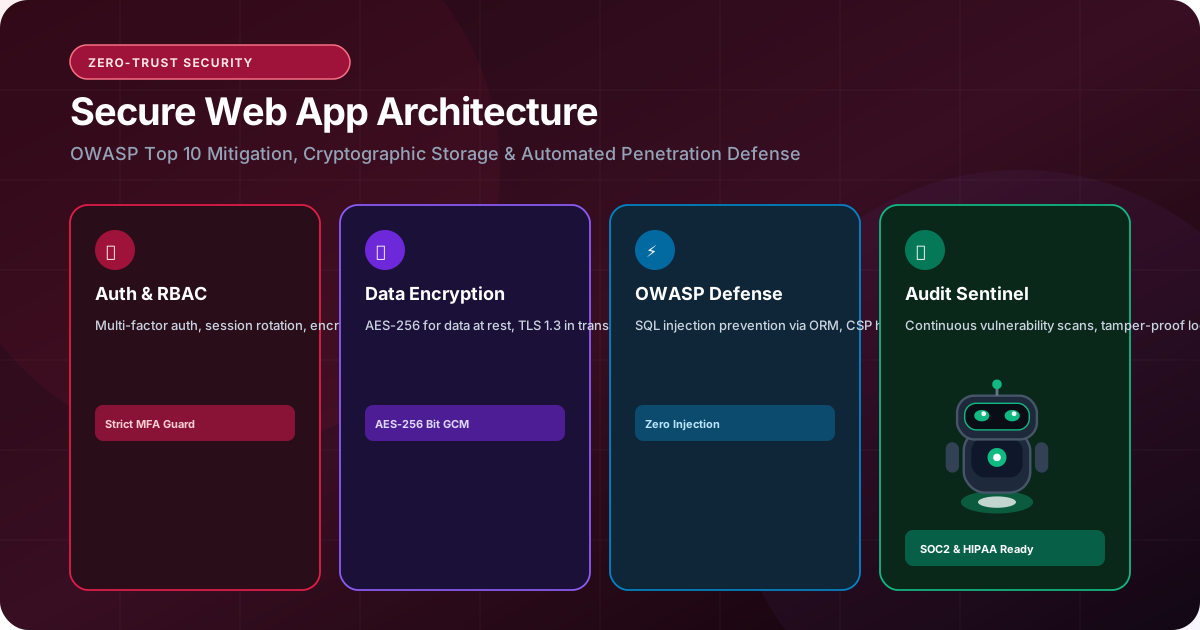
Secure web application development requires a defense-in-depth architecture: eliminating SQL injection through parameterized ORMs, storing authentication sessions in HttpOnly Secure SameSite=Strict cookies, enforcing strict Content Security Policies (CSP), isolating secrets in cloud key vaults, and implementing zero-trust Role-Based Access Control (RBAC).
1. The Modern Threat Landscape for Business Software
Why small and mid-sized enterprises are now primary cyber targets
A dangerous misconception among business founders is: 'Our company is not large enough for hackers to care about us.'
In modern cybersecurity, attacks are rarely launched by targeted human hackers manually inspecting your website. Instead, automated botnets continuously scan IPv4 and IPv6 address ranges across the globe, executing automated exploit scripts against thousands of domains simultaneously.
If your web application runs on outdated software with unpatched vulnerabilities, the automated script breaks in, exfiltrates customer records, injects SEO spam or crypto-miners, and locks your database for ransom.
Security is about eliminating the low-hanging architectural flaws that automated tools target.
2. Mitigating the OWASP Top 10 Vulnerabilities
The definitive global standard for web application security defense
The Open Web Application Security Project (OWASP) maintains the industry-standard benchmark of the ten most critical web security vulnerabilities:
• Broken Access Control: The #1 vulnerability in modern web apps. Occurs when an application fails to verify whether an authenticated user has permission to view a specific record (e.g., changing the URL from /api/invoice/100 to /api/invoice/101 and seeing another company's invoice). We enforce strict database-level Row-Level Security (RLS) to ensure users can only query their own records.
• Cryptographic Failures: Exposing sensitive data in transit or at rest. We enforce TLS 1.3 encryption across all network traffic, HSTS preloading, and AES-256 database column encryption on sensitive PII.
• Injection Flaws (SQLi & XSS): Attackers injecting malicious SQL commands into form fields or executing rogue scripts in other users' browsers. We eliminate SQL injection through parameterized ORMs and neutralize Cross-Site Scripting (XSS) through framework-level HTML escaping in React.
3. Secure Authentication: Tokens, Sessions & MFA
Why localStorage is a security anti-pattern and how to store session tokens safely
One of the most widespread security flaws in modern web development is storing authentication JWT tokens in browser localStorage. Any third-party script or Cross-Site Scripting (XSS) vulnerability can read localStorage and exfiltrate user credentials.
At RankVRA, we implement strict, secure authentication protocols:
• HttpOnly, Secure, SameSite=Strict Cookies: Authentication tokens are stored inside browser cookies that JavaScript cannot read (HttpOnly), that only transmit over encrypted HTTPS (Secure), and that are never sent during cross-site requests (SameSite=Strict, preventing Cross-Site Request Forgery / CSRF).
• Cryptographic Password Hashing: User passwords are never stored in plaintext. We hash passwords using Argon2id or bcrypt with high computational work factors, making brute-force dictionary attacks impossible.
• Multi-Factor Authentication (MFA): Enforcing time-based one-time passwords (TOTP via Google Authenticator or SMS/WhatsApp OTP) for administrative and privileged user accounts.
4. Database & API Security: Parameterization and Rate Limits
Protecting the persistence tier and preventing API abuse
Your database is your company's crown jewel. Securing the database requires two non-negotiable architectural protections:
1. Parameterized Queries & Strict ORMs: Utilizing modern query builders like Prisma or SQLAlchemy that treat all user input as raw literal values rather than executable code. Even if a user enters "' OR '1'='1' --" into a username field, the database engine treats it as a literal string name, completely neutralizing SQL injection.
2. Redis-Backed Token-Bucket Rate Limiting: Protecting public API routes and login endpoints against brute-force credential stuffing. If an IP address attempts more than 5 failed login attempts in 60 seconds, our Redis middleware temporarily bans requests from that origin for 15 minutes.
5. Hardening Browser Defenses: Security Headers & CSP
Locking down the browser execution sandbox with defense-in-depth headers
Every HTTP response emitted by your web application should include strict security headers that instruct modern browsers to enforce defensive execution rules:
• Content-Security-Policy (CSP): Restricting the exact domains from which scripts, stylesheets, fonts, and images can be loaded, preventing unauthorized third-party scripts from executing.
• Strict-Transport-Security (HSTS): Forcing browsers to only communicate over encrypted HTTPS for the next 365 days, preventing man-in-the-middle downgrade attacks.
• X-Frame-Options: DENY: Preventing malicious external websites from embedding your application inside an invisible <iframe> to steal user clicks (clickjacking defense).
• X-Content-Type-Options: nosniff: Preventing the browser from MIME-sniffing a response away from the declared content-type, stopping executable uploads disguised as images.
6. Security Threats vs Defensive Architecture Matrix
A comprehensive mapping of common web attacks and architectural defenses
The table below details how modern web engineering neutralizes prevalent cyber threats:
| Threat / Attack Vector | Attack Mechanism | Engineering Remediation | Verification Standard |
|---|---|---|---|
| Broken Access Control (IDOR) | Modifying record ID parameters in URLs/APIs | Database Row-Level Security (RLS) + Session RBAC | Automated multi-role integration tests |
| SQL Injection (SQLi) | Injecting malicious SQL syntax into form fields | Parameterized queries via Prisma ORM / SQLAlchemy | Static code analysis & SonarQube audit |
| Cross-Site Scripting (XSS) | Injecting malicious JavaScript into page DOM | Strict CSP headers + React native JSX escaping | CSP evaluation via Google CSP Evaluator |
| Cross-Site Request Forgery (CSRF) | Trick user into submitting unauthorized actions | SameSite=Strict cookies + Anti-CSRF tokens | Session header verification |
| Credential Stuffing / Brute Force | Automated bots guessing thousands of passwords | Redis token-bucket rate limiting + MFA | Automated bot simulation testing |
| Secret Key Exfiltration | Accidental leakage of API keys in client bundles | Environment variable isolation + Server-only code | GitHub secret scanning + pre-commit hooks |
7. The 10-Point Enterprise Web Security Checklist
Non-negotiable verification points before deploying business software to production
Before launching any custom software or web application, ensure your technical team verifies each of these points:
1. Are all session cookies configured with HttpOnly, Secure, and SameSite=Strict flags?
2. Does the application enforce HTTPS with a valid TLS 1.3 certificate and HSTS preload headers?
3. Is the Content Security Policy (CSP) active and verified against Google's CSP Evaluator?
4. Are all database queries parameterized with zero raw string concatenation?
5. Does the application implement strict Role-Based Access Control verified at the API route level?
6. Are login and sensitive endpoints protected by Redis-backed rate limiting?
7. Are production environment variables and database credentials stored in an encrypted cloud vault?
8. Are file uploads restricted by MIME-type validation and stored in private cloud buckets with signed URLs?
9. Are third-party npm/pip dependencies audited for known vulnerabilities (via npm audit / Snyk)?
10. Is an automated backup and disaster-recovery plan documented and verified with quarterly test restores?
The Bottom Line & Next Steps
Building a secure web application is not about achieving theoretical perfection; it is about implementing disciplined, multi-layered defenses that make breaking into your platform mathematically and computationally prohibitive. By following OWASP standards, securing session tokens in HttpOnly cookies, parameterizing database queries, and enforcing zero-trust access controls, you safeguard your business assets and reassure enterprise clients that their data is protected. Discuss your web application security requirements with RankVRA today.
Questions Business Leaders Ask About secure web application development
How do we know if our existing web application has security vulnerabilities?▾
We conduct professional Vulnerability Assessments and Penetration Testing (VAPT). We review your source code, audit API endpoint authentication, inspect database query sanitation, and simulate real-world attacks to identify and remediate security vulnerabilities before malicious actors find them.
Is Next.js inherently secure?▾
Next.js provides excellent native security defaults—such as automatic XSS escaping in JSX and server-side code separation via Server Components. However, security ultimately depends on how developers implement authentication, database queries, and authorization rules.
What is Row-Level Security (RLS) in databases?▾
Row-Level Security is a database-native security feature (supported by PostgreSQL) where access policies are enforced directly at the database engine level. Even if an engineer forgets to check permissions in the backend API code, the database will refuse to return any rows that do not belong to the authenticated user.
Written by Naveen Panchal
AuthorFounder & Lead Technical Architect, RankVRA
Naveen Panchal is the Founder and Technical Director of RankVRA. He specializes in full-stack web engineering, Next.js architecture, and high-performance digital systems for clients across the US, UK, Canada, and India.
Explore Core Commercial Capabilities
Vulnerability audits & OWASP application hardening
Node.js, Python & scalable database architecture
Bespoke business portals & operational software
Unified client-to-database engineering
Multi-tenant software-as-a-service platforms
- OWASP Foundation: OWASP Top 10 Web Application Security RisksOfficial Reference
- Mozilla Security Team: Mozilla Observatory Web Security GuidelinesOfficial Reference
- National Institute of Standards and Technology: NIST Special Publication 800-63B: Digital Identity GuidelinesOfficial Reference
Discuss Your Secure Web Application
Protect your customer records, financial transactions, and proprietary business software from cyber vulnerabilities. Consult with RankVRA to architect an enterprise-hardened web platform.
Related Growth Blueprints
Explore more strategic articles from the RankVRA engineering desk.
What Is Backend Development and Why Is It Important for Modern Web Applications?
Demystify backend development. Discover how server architectures, relational databases, Node.js, Python, and OWASP security protect and scale business web applications.
Custom Web Application Development: When Should a Business Build a Custom Web App?
When should a business build custom web applications instead of subscribing to SaaS? Learn how custom portals, wholesale dashboards, and bespoke workflows deliver compounding ROI.
How to Integrate Payment Gateways Into a Website or Web Application
Learn how to integrate payment gateways securely. Master Stripe, Razorpay, webhook verification, recurring billing, and PCI compliance for websites and web apps.